A signed reference receipt
The specimen the strip above verifies: a canonical body, its digest, and a signature the public key inside the receipt can check. Synthetic data; no customer evidence.
- Format
governed-receipt/v1Ed25519
Turn scattered artifacts into a clear, connected audit. AI prepares the evidence. Your team makes the call.
All interactive user accounts must use a password of at least 14 characters.
A stated parameter, with its original passage attached.
Design evidence onlyAI proposes requirement mappings. The source travels with every suggestion.
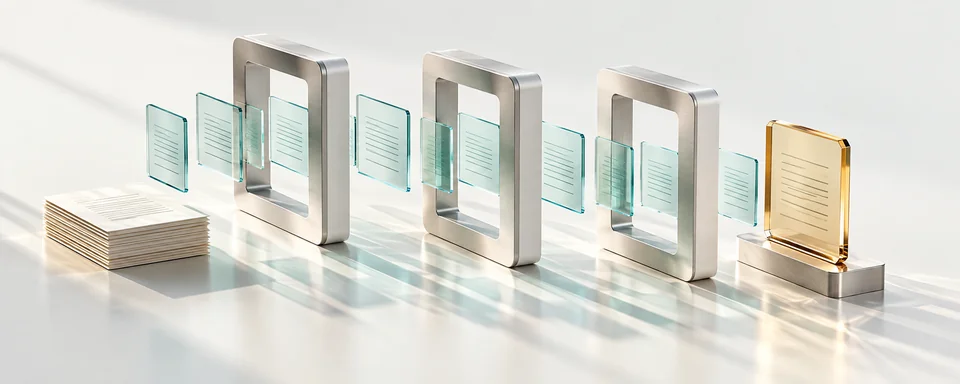
A signed synthetic reference specimen — no customer evidence or production custody. Your browser verifies the actual signature with no account or network call.
governed-receipt/v1 · 2026-08-24Proof, not promises
Each card is a real object with its own record. The counts are read from the source at build time, never typed.
The specimen the strip above verifies: a canonical body, its digest, and a signature the public key inside the receipt can check. Synthetic data; no customer evidence.
governed-receipt/v1Ed25519One HTML file that recomputes a receipt's chain and signature on the reader's own machine. Save it once; it needs no account and makes no network call.
offline-verifier.html40 KB · self-containedOne framework release ingested from its issuing source and normalized into a catalog, with the source digest retained so the pin can be re-checked.
01f37cf90e…9bc062NIST OSCAL Content v1.5.0 · OSCAL 1.2.2Every regime the product tracks, with its issuing authority, current edition, and product standing. Only a regime with a catalog behind it is counted as one.
controlframe.framework-registry.v3generated 2026-08-30Built for accountability
AI prepares the work. Your team controls what moves forward.
A named reviewer decides whether the proposed action may proceed. AI cannot approve its own work.
Illustrated workflow · no live run or approval
| Safeguard | When it applies | Who or what decides | Record retained | If it cannot proceed |
|---|---|---|---|---|
| Held write | An agent proposes a write | A named reviewer | Held-for-review record in the decision passport | Refused, or approved and re-run |
| Artifact intake | A file enters quarantine | Pinned scan policy | Scan record with engine and definitions digests | Held in quarantine |
| Package release | A package is submitted for release | Named human sign-off | Hash-pinned release record | Held, with the blocking gate named |
| Recipient access | A recipient opens a package | A live grant | Grant manifest and activation window | Refused when revoked or expired |
| Runner admission | A private runner asks for work | Control-plane token binding | Worker profile and package digest in the token | Denied |
| Evidence freshness | An artifact ages past policy | Freshness policy | Stale controls listed in the sweep receipt | Recollect at source |
A verified record proves integrity. Evidence sufficiency, approval, package eligibility, and release each require their own checks.
By the numbers
Assurance intelligence · official sources
The changes that affect your audit, with the original sources and practical next steps.
Browse source briefingsThe Consolidated Rules for 2026 move FedRAMP toward persistently maintained security-decision records, reusable certification data, and human- and machine-readable packages, with the Class B and Class C pipeline scheduled to open August 31, 2026.
Connect each security decision to its measure, validation, independent review, change history, and released package rather than rebuilding a static folder for every agency.
Commission enforcement powers apply to provisions already in force, while transparency duties apply from August 2026 and the amended high-risk deadlines move to December 2027 and August 2028 by system class.
The initial public draft of SP 1353 illustrates AI-assisted CSF analysis, planning, implementation, and monitoring while calling for precautions and continuous evaluation and improvement.
Version 11.8 continues requirement-statement consolidation and refreshes mappings including PCI DSS v4.0.1 and the AICPA SOC 2 Trust Services Criteria.
01 / The ControlFrame difference
The defensible system is the chain around intelligence: source-native methods, bounded execution, human-held authority, and one governed record operators and authorized recipients can inspect from their own view.
Four connected layers · one decision recordVersioned procedures bind scope, approved sources, tools, budgets, and human gates before work begins.
Collection and testing operate inside declared authority. Exceptions route to people; agents do not inherit release power.
Customer-controlled endpoint routing exists today. The purpose-built private assurance model for evidence classification, extraction, and drafting remains in development.
The passport is the portable decision record. For eligible releases, its governed-receipt schema binds identity, model trace, human disposition, and chain state for offline verification.
Compose the method, then see how an assurance team carries it into fieldwork.
Continuous assurance system
Observe approved sources, collect through bounded jobs, preserve artifact identity, propose control mappings, route exceptions, and release only through named human authority. The reference below shows the operating contract; tenant execution stays inside activated workspaces.
Credentials and supervised MFA remain inside the approved customer boundary.
Every configured job carries its source, expected artifact contract, control context, reviewer state, and release boundary.
Freshness and change signals
observingApproved source journeys
04 capturesDigest, context, custody
verifiedNative control + reuse candidates
reviewArtifacts, documents, versions, freshness, owners
governed recordSource obligation, control IDs, reviewed projections
traceable reuseCompleteness, exceptions, approvals, release state
human gatedEvidence reuse remains advisory until an authorized reviewer confirms sufficiency.




Each mark names a connector definition in the registry. A connection exists for an organization only once its own credential has validated against the provider.
Recorded product evidence
Follow one synthetic healthcare enrollment journey from browser interaction to captured artifact, mapped control, and an explicit human review boundary.
Product recording · synthetic reference
The recording shows the browser journey. The companion trace illustrates capture, artifact identity, and the human-release boundary; it is not a signed custody record.
Framework modules
Each tracked regime carries explicit source and product standing. Where a catalog and method are released, one governed cross-reference layer can propose reuse without presuming the target reviewer’s conclusion.
A source-backed learning instrument
Explore one real release from issuing source to normalized catalog, retained assessment context, and named human acceptance. Every station carries its own status; the path never fills a missing fact with a claim.
Open the Catalog ObservatoryRelease 5.2.0
Operating leverage
Whether the audit is SOC 2, HITRUST, PCI DSS, HIPAA, or CMS EDE, the handling lives in the evidence. Adjust the hours-first model to your own program and see the effort returned; then confirm it against observed work in a scoped pilot.
Authority boundary
Qualified assessors, CPA firms, certification bodies, and other authorized third parties keep their existing authority. ControlFrame makes the evidence easier to inspect; it does not certify the customer.Enter the proof room
In the family
ControlFrame is the control plane beside two sibling properties: the LockedIn Labs FDE platform, which runs engagements, and the FDE Benchmark, which measures the work. ControlFrame is where the controls around that work are held and proved. All three are LockedIn Labs properties; these links go to our own sites. About ControlFrame
Pilot one evidence lane
We will map its systems, labor, controls, authority gates, and measurable pilot outcome in one executive working session.